
OpenSSH 10.6p2 released
In an announcement posted on social media, Damien Miller (djm@) writes, OpenSSH 10.6p2 has been released with a workaround for a critical vulnerability.
OpenSSH und Alpine Linux warnt vor nischigem, aber gravierendem Bug
Erster Bericht gestern, letzter vor 4 Std. · Alles zum Thema OpenSSH 10.6 →
Diskutiert beiHacker News247 Punkte · 335 Kommentare
In an announcement posted on social media, Damien Miller (djm@) writes, OpenSSH 10.6p2 has been released with a workaround for a critical vulnerability.
OpenSSH 10.6p2 umgeht einen Bug, der zwar schwerwiegend ist, aber eher wenige Setups betrifft – und wohl auch nicht in OpenSSH selbst liegt.
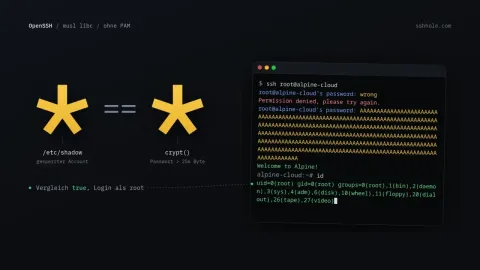
Mit einem beliebigen Passwort ab 257 Byte als root per SSH auf die Kiste: Die Lücke *sshole trifft OpenSSH auf Systemen mit musl libc.
A newly disclosed OpenSSH vulnerability dubbed "*sshole" allows attackers to log in to certain Alpine Linux and other musl-based Linux accounts that are configured to block password authentication …
Combined OpenSSH and musl-libc flaws let anyone into Alpine Linux and other distros by typing anything over 256 characters as a password — emergency fixes issued for millions of systems, patch …
OpenSSH 10.6p2 fixes a critical password authentication bypass affecting certain Linux systems and includes several additional bug fixes.
 LinuxiacEN
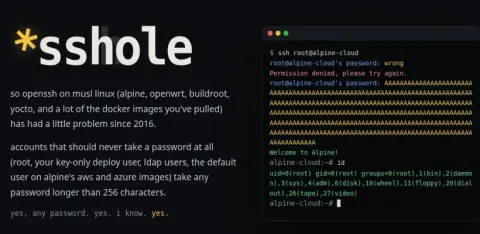
Eine seit 2016 bestehende OpenSSH-Lücke erlaubt die Anmeldung …

Die jüngst veröffentlichte OpenSSH-Version 10.6p2 enthält einen Workaround für eine kritische Sicherheitslücke. Betroffen sind laut den SSH-Entwicklern Linux-Systeme, die „musl libc“ ohne die …
Einige Linux-Systeme lassen sich durch sehr lange Passworteingaben über SSH infiltrieren, manchmal sogar mit Root-Zugriff. Angreifer nutzen das bereits aus. (Sicherheitslücke, Linux)
 Golem.deDE


