
OpenSSH 10.6p2 released
In an announcement posted on social media, Damien Miller (djm@) writes, OpenSSH 10.6p2 has been released with a workaround for a critical vulnerability.
OpenSSH 10.6p2 Released to Fix Critical Password Authentication Bypass
First report yesterday, latest 18 h ago · Everything on OpenSSH 10.6 →
Discussed onHacker News247 points · 335 comments
In an announcement posted on social media, Damien Miller (djm@) writes, OpenSSH 10.6p2 has been released with a workaround for a critical vulnerability.
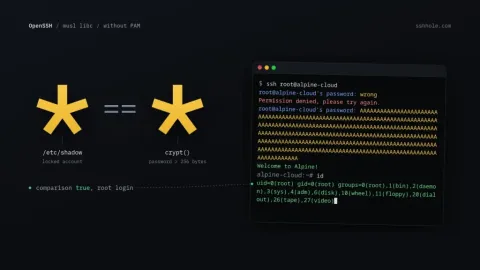
Log in as root via SSH with any password longer than 256 bytes: the *sshole vulnerability hits OpenSSH on systems with musl libc.
A newly disclosed OpenSSH vulnerability dubbed "*sshole" allows attackers to log in to certain Alpine Linux and other musl-based Linux accounts that are configured to block password authentication …
Combined OpenSSH and musl-libc flaws let anyone into Alpine Linux and other distros by typing anything over 256 characters as a password — emergency fixes issued for millions of systems, patch …
OpenSSH 10.6p2 fixes a critical password authentication bypass affecting certain Linux systems and includes several additional bug fixes.
 LinuxiacEN


