
CISA says max severity GitLab flaw now exploited in the wild
Attackers have started exploiting a maximum-severity GitLab vulnerability patched earlier this month, according to the US Cybersecurity and Infrastructure Security Agency (CISA).
Attackers have started exploiting a maximum-severity GitLab vulnerability patched earlier this month, according to the US Cybersecurity and Infrastructure Security Agency (CISA).
GitLab has released security patches for a maximum-severity Regular Expression Compiler flaw that can let remote attackers run arbitrary code on vulnerable servers.
GitLab has released security updates addressing a critical vulnerability that could allow attackers to execute code without authentication.
 Datenschutz
 Verschlüsselung
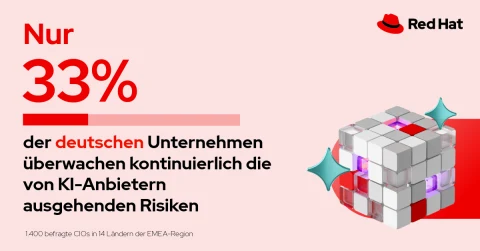 Lieferkette
 Linux-Kernel

